
Home
/
techsearch
/
techsearch-case-study-mdr
How an Australian Aged Care Provider Compared 8 MDR Vendors and Discovered a Better-Fit Supplier
Published by StrategyMix on 03 November 2026
An Australian aged care organisation used StrategyMix TechSearch to evaluate 8 Managed Detection and Response (MDR) providers.
Rather than relying solely on existing supplier relationships, the buyer was able to evaluate a broader range of providers against a common set of requirements.
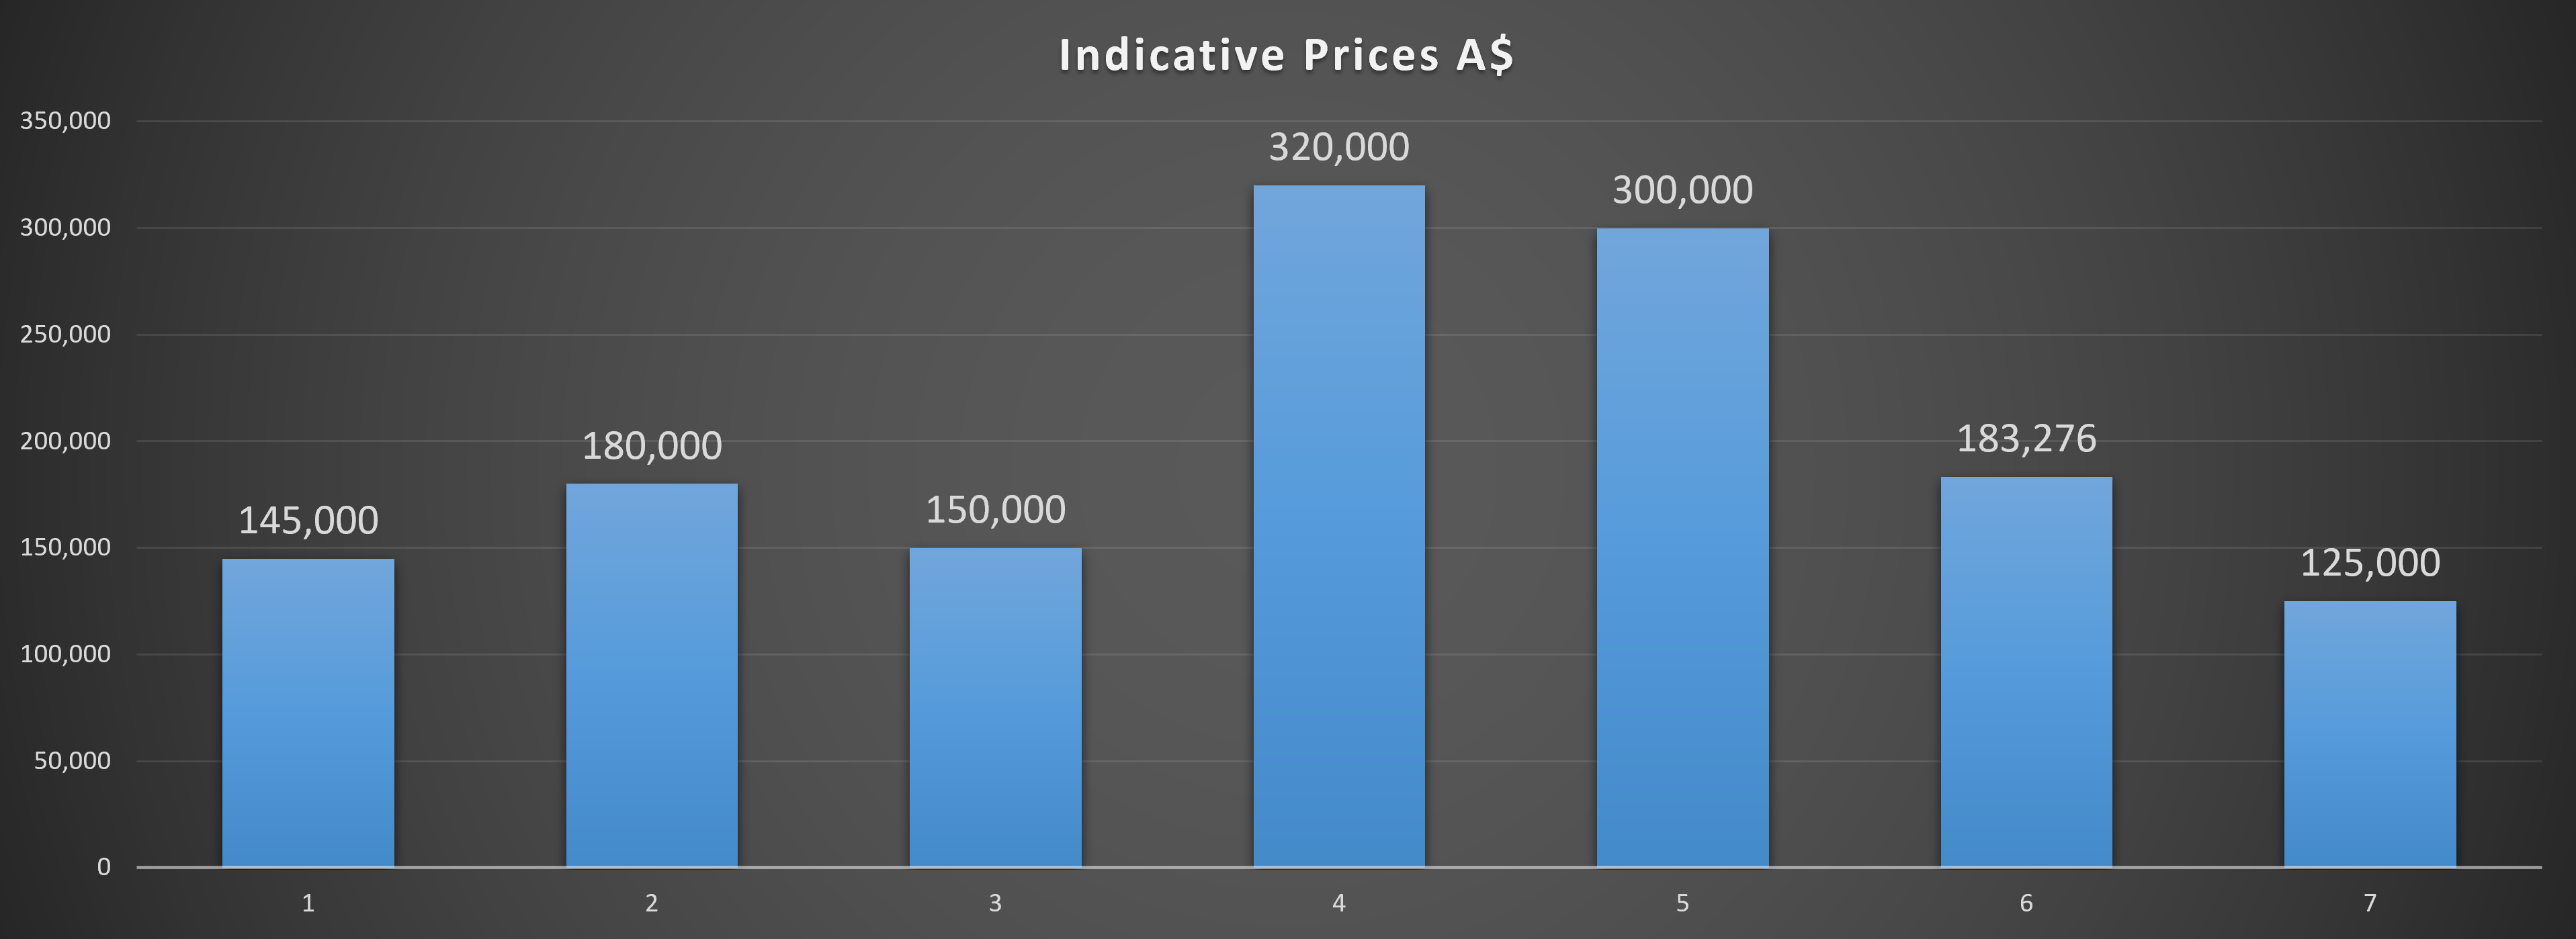
The responses revealed a significant variation in indicative pricing and introduced the buyer to a supplier they had not previously considered.
Summary Result
8
Detailed Vendor Responses
A$125,000–320,000
Indicative Pricing for the same brief
An unexpected supplier
The buyer awarded the contract to a supplier they hadn't previously known and would probably not have engaged without TechSearch.
Buyer Quote
I am very pleased with the results I have had from the new TechSearch functionality.
As you can see, I have received 8 very good responses, and this has certainly given me some very relevant options to evaluate.
The alternative that I was following was to contact vendors who I was familiar with, but the solutions that they have proposed are well beyond our budget. TechSearch on the other hand has given me vendors who are at least offering something within the scope of what I can afford.
Ian Bedson, Cyber Security Advisor, ACH Group
Buyer Profile
Job Role:
Cyber Security Manager
Industry:
Not For Profit
Headcount:
501 to 1000
Revenue:
A$ 101 to 500 Million
Region:
Australia South (SA/VIC/TAS)
Buyer Search Summary
The buyer’s requirements
- 24/7 security monitoring.
- Incident response support.
- Integration with existing security investments.
- Potential SIEM replacement.
- Flexible incident response pricing.
View Full Buyer Requirements
Questions
What the buyer wanted vendors to address
Q1. Can you ingest and correlate data from CrowdStrike, Mimecast, Netskope, and Graylog?
Q2. Can you enrich alerts with threat intelligence or contextual data from these platforms?
Q3. How do you prioritise alerts and reduce false positives?
Q4. Do you offer services to enhance or replace Graylog with a more scalable SIEM?
Q5. Do you offer retainer-based IR services or on-demand support?
Vendor Responses
Response: SecMatters
Solution Summary
- Provides comprehensive 24×7 cybersecurity monitoring, detection, and incident response with integration across tools like CrowdStrike, Mimecast, Netskope, and Graylog.
- Enhances alert accuracy by enriching data with threat intelligence, using risk-based prioritization to reduce false positives and deliver actionable insights.
- Offers flexible incident response models and supports optimization or transition to scalable SIEM platforms such as Microsoft Sentinel, preserving client control and affordability.
View Full Response
https://www.strategymix.com.au/secmatters-cyber-security-monitoring-incident-response-aged-care
Response: StickmanCyber
Solution Summary
- Delivers a comprehensive 24×7 Managed Detection and Response using Google SecOps platform with integrated SIEM, SOAR, AI-driven triage, and 12 months of hot log storage for enterprise-wide threat visibility and automation.
- Supports native ingestion and enrichment of alerts from CrowdStrike, Mimecast, Netskope, plus custom integration options for Graylog, using threat intelligence from Google, Mandiant, and multiple contextual sources for precise alert prioritization and reduced false positives.
- Provides scalable Graylog replacement and migration services, with flexible Incident Response offerings to enhance client security posture and streamline operations on a predictable fixed pricing model.
View Full Response
https://www.strategymix.com.au/stickmancyber-cyber-security-monitoring-incident-response-aged-care
Response: Cythera
Solution Summary
- Delivers a sovereign, fully onsite ANZ SOC staffed by Level 3 engineers who proactively manage and triage alerts, ensuring rapid response (MTTR of 23 minutes) with tailored rule tuning to minimize false positives and optimize SIEM log ingestion and costs.
- Integrates advanced and locally-sourced threat intelligence, including customer-supplied and ACSC feeds, enhancing detection quality with unique in-house sharing across diverse Australian customers and continuous threat hunting capabilities.
- Provides flexible, comprehensive services spanning managed SOC, incident response retainers, and scalable SIEM platforms (CrowdStrike, Microsoft Sentinel, Rapid7, LogRhythm) with an embedded lead analyst model to act as an extension of the buyer’s team.
View Full Response
https://www.strategymix.com.au/cythera-cyber-security-monitoring-incident-response-aged-care
Response: Blue Apache Pty Ltd
Solution Summary
- Delivers a comprehensive, fully integrated MDR solution with 24×7 SOC monitoring, advanced threat hunting, and unlimited incident response including deep forensic capabilities for thorough investigations.
- Provides seamless ingestion, correlation, and enrichment of data from multiple security platforms (CrowdStrike, Mimecast, Netskope, Graylog) with strong alert prioritization to reduce false positives and deliver actionable insights.
- Ensures compliance with Australian data sovereignty, scalable protection for large Age Care environments, and includes strategic advisory services with legally binding, financially backed SLAs to guarantee performance and accountability.
View Full Response
https://www.strategymix.com.au/blue-apache-cyber-security-monitoring-incident-response-aged-care
Response: Secure Agility
Solution Summary
- Delivers a comprehensive 24×7 managed SOC leveraging Arctic Wolf MDR with deep integration and correlation of data from CrowdStrike, Mimecast, Netskope, and Graylog, enabling broad and unified threat detection.
- Enhances alert accuracy by enriching alerts with global threat intelligence, contextual data, and local business relevance, reducing false positives through multi-stage validation and expert analyst triage.
- Provides flexible incident response options including retainer and on-demand services, plus scalability with options to enhance or replace Graylog with a fully managed cloud-native SIEM for streamlined operations.
View Full Response
https://www.strategymix.com.au/secure-agility-cyber-security-monitoring-incident-response-aged-care
Response: Cyber83
Solution Summary
- Delivers tailored 24×7 cybersecurity monitoring and incident response with local Australian expertise combined with global resources, ensuring compliance and seamless care delivery support.
- Integrates and enriches alerts from existing tools like CrowdStrike, Mimecast, Netskope, and Graylog, using advanced analytics and Cyber83’s unique threat intelligence for precise, actionable insights.
- Provides flexible, embedded incident response services and scalable SIEM upgrades to Rapid7 InsightIDR, enhancing detection accuracy, reducing false positives, and improving operational efficiency.
View Full Response
https://www.strategymix.com.au/cyber83-cyber-security-monitoring-incident-response-aged-care
Response: Cynet
Solution Summary
- Delivers 24×7 co-managed cybersecurity monitoring with Cynet’s AI-driven XDR platform, ensuring fast, accurate threat detection and response while reducing alert fatigue in aged care and NFP sectors.
- Seamlessly integrates and enriches data from existing tools like CrowdStrike, Mimecast, Netskope, and Graylog, enabling consolidated threat visibility and flexible SIEM enhancement or replacement.
- Offers adaptable incident response models—including retainer and pay-per-incident options—with ransomware warranty coverage and proactive services tailored to operational continuity and budget control.
View Full Response
https://www.strategymix.com.au/cynet-cyber-security-monitoring-incident-response-aged-care
Response: AUCyber
Solution Summary
- Delivers continuous 24×7 monitoring and incident response from an Australia-based SOC, using AI-driven SentinelOne Singularity Platform for enhanced threat detection and automated response.
- Integrates seamlessly with existing tools like CrowdStrike, Mimecast, Netskope, and supports migration from Graylog to enable centralized, scalable SIEM capabilities.
- Offers flexible incident response options, including retainer and on-demand models, enriched alerts with threat intelligence, and risk-based prioritization to reduce false positives and accelerate investigation.
View Full Response
https://www.strategymix.com.au/aucyber-cyber-security-monitoring-incident-response-aged-care
What this TechSearch Case Study Demonstrates
This case study illustrates how TechSearch can help IT buyers move beyond their existing supplier relationships, evaluate a broader range of solutions and compare indicative pricing against consistent requirements.
By inviting multiple vendors to respond to the same brief, buyers can discover alternative providers and make more informed purchasing decisions.
This gives the article a proper conclusion and reinforces the main value proposition.